Why ATM Security Needs a New Approach in the Digital Banking Era
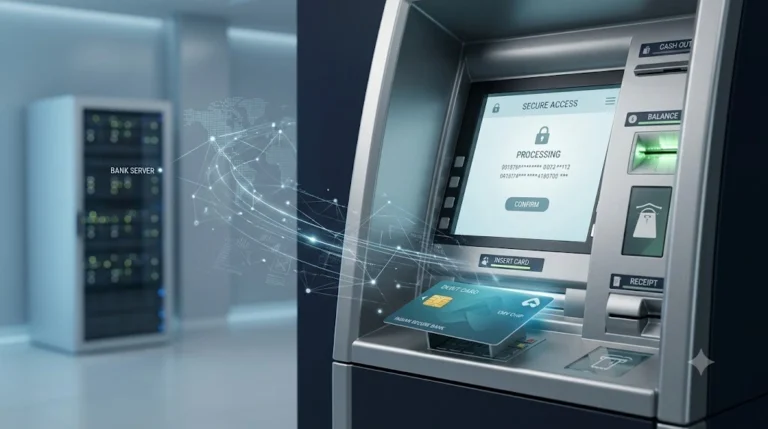
ATMs remain one of the most critical customer-facing assets for financial institutions. Operating across thousands of geographically distributed locations—from metropolitan cities to remote rural areas ATMs provide essential banking services while handling sensitive financial transactions.
However, as banks continue accelerating digital transformation across enterprise IT environments, ATM infrastructure often presents unique operational and cybersecurity challenges. Unlike traditional enterprise endpoints, ATMs operate in distributed environments with limited physical accessibility, specialized configurations, and strict availability requirements.
With increasing cyber threats and evolving regulatory expectations, financial institutions must rethink how they manage security, compliance, and operational efficiency across their ATM ecosystem.
The Challenges of Traditional ATM Patch Management
Historically, ATM patching has relied heavily on manual processes, vendor coordination, and scheduled maintenance activities. While this approach may have worked in smaller environments, it becomes increasingly challenging as ATM networks expand.
Financial institutions face several key challenges :
Limited Visibility Across Distributed ATM Networks
Maintaining real-time visibility into patch levels, operating system versions, and security compliance across thousands of remote devices is complex. Lack of centralized visibility can result in unidentified vulnerabilities and compliance gaps.
Dependency on Manual Intervention
Traditional patching processes often require coordination between internal teams, ATM vendors, and field engineers. This increases operational complexity and makes timely deployment of critical updates difficult.
Extended Vulnerability Exposure
Security patches addressing critical vulnerabilities must be deployed quickly. Delayed patch cycles increase the risk of exploitation, especially across devices operating in remote and publicly accessible locations.
Increasing Regulatory Expectations
Financial institutions are under growing pressure to demonstrate strong cybersecurity governance, continuous compliance monitoring, and audit readiness. Manual reporting processes are no longer
sufficient for large-scale environments.
Moving Towards Automated and Policy-Driven Patch Management
Modern ATM security requires a shift from reactive maintenance to proactive, automated compliance management.
An effective automated patch management framework enables organizations to:
Centralize Endpoint Visibility
A unified management approach provides complete visibility into ATM assets, operating systems, installed software, patch status, and compliance posture.
Policy-driven automation allows organizations to define patch schedules, approval workflows, deployment rules, and rollback mechanisms while minimizing operational disruption.
Improve Compliance Readiness
Real-time dashboards and automated reporting provide security teams with continuous insight into compliance status and help simplify regulatory audits.
Reduce Operational Dependency
Remote automation reduces reliance on onsite interventions and vendor coordination, enabling faster response to security requirements.
Business Benefits of Automated ATM Patch Management
By adopting automation-driven endpoint management practices, financial institutions can achieve significant improvements:
Improved Operational Efficiency
Automated patch deployment eliminates repetitive manual activities and reduces dependency on field teams, enabling faster and more consistent patch cycles.
Enhanced Security Posture
Faster deployment of critical security updates helps reduce vulnerability exposure and strengthens protection against emerging cyber threats.
Continuous Compliance Visibility
Centralized monitoring and reporting provide audit-ready evidence of security controls and compliance status.
Reduced Operational Risk
Standardized processes, automated workflows, and controlled deployments help minimize errors and ensure consistent security practices across distributed ATM networks.
The Future of ATM Security: From Endpoint Management to Intelligent Governance
The future of ATM infrastructure management lies in combining automation, centralized visibility, and intelligent compliance monitoring. As cyber threats become more sophisticated and regulatory requirements continue to evolve, financial institutions must move beyond manual processes and adopt proactive security operations.
Automated patch management is no longer just an operational improvement—it is a strategic capability that enables banks to protect critical customer touchpoints, strengthen cyber resilience, and deliver secure digital banking experiences.